Definition and Scope of Article 14
Article 14 of Regulation (EU) 2024/1689, known as the EU Artificial Intelligence Act, is located in Section 2 of Chapter III, which is dedicated to the requirements for high-risk AI systems. Contrary to what some secondary translations suggest with the title 'Human Oversight', the official consolidated text from the European Commission identifies this article specifically as the 'Risk Management System'. This precision is fundamental for compliance, as it establishes a technical and organizational obligation distinct from human oversight, which is regulated in other related sections or articles.
The regulation obliges providers of high-risk AI systems to establish, document, implement, and maintain a continuous risk management system throughout the entire lifecycle of the system. This requirement is not static; it demands a dynamic of risk identification, assessment, mitigation, and monitoring that adapts to changes in the system, its usage environment, or the emergence of new risks. The official primary source, the European Commission's AI Act Explorer, confirms the existence of this provision within the current legal structure, which has been amended by Regulation (EU) 2026/1744 (Digital Omnibus on AI). This implies that compliance teams must verify the most recent consolidated version.
The distinction between risk management and human oversight is not merely semantic but operational, as it dictates the specific technical controls and organizational structures that providers must implement. While human oversight focuses on the capability of natural persons to monitor, interpret, and intervene in the system's operation, the risk management system required by Article 14 encompasses the broader lifecycle activities necessary to ensure that the system remains safe and effective. This includes the systematic identification of potential harms, the evaluation of their likelihood and severity, and the implementation of measures to mitigate them. Consequently, compliance with Article 14 requires a holistic approach that integrates technical documentation, process controls, and organizational responsibilities, ensuring that the risk management system is not an isolated procedure but a core component of the system's development and maintenance strategy.
Furthermore, the requirement to maintain a continuous risk management system implies that providers must establish clear internal governance structures to oversee this process. This involves defining roles and responsibilities for risk identification, assessment, and mitigation, as well as establishing procedures for documenting and reporting risks to relevant stakeholders. The continuous nature of the obligation means that providers must regularly review and update their risk management processes to reflect changes in the system, its usage environment, or the emergence of new risks. This ongoing process ensures that the risk management system remains effective and relevant throughout the system's lifecycle, thereby supporting the overall objective of the AI Act to ensure that high-risk AI systems are safe, transparent, and trustworthy.
The Continuous Risk Management System
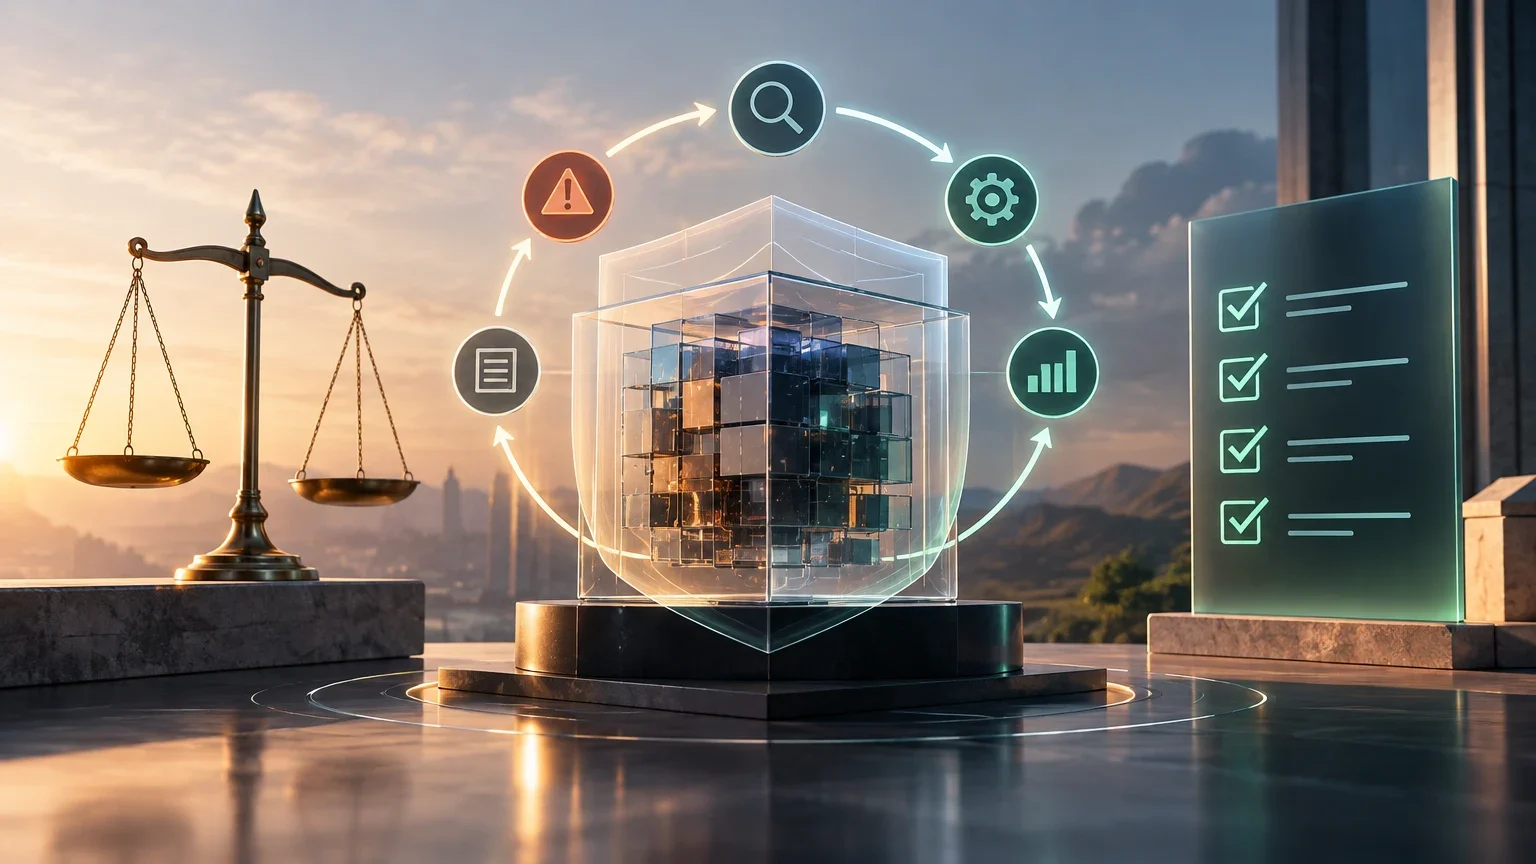
The mechanism required by Article 14 is not limited to a one-off audit before launch. It is an iterative process covering four main phases: risk identification, assessment of their probability and severity, implementation of mitigation measures, and continuous monitoring. 'Continuity' is the key word: the system must be capable of detecting when a previously mitigated risk becomes relevant again or when a new risk not contemplated in the design phase emerges.
This obligation is directly linked to the technical documentation required by Article 11 and detailed in Annex IV. The provider must not only have the process but must be able to demonstrate to the competent authorities that the risk management system is operational and that the decisions taken are documented. A lack of traceability in the evolution of risks can be considered a breach, even if the system functions correctly at the time of inspection.
The iterative nature of the risk management process required by Article 14 necessitates a robust framework for documenting and tracking risks over time. This framework must enable providers to capture the evolution of each identified risk, including changes in its probability, severity, and the effectiveness of mitigation measures. Such documentation is essential for demonstrating compliance with the regulation, as it provides a clear audit trail that can be reviewed by competent authorities. The ability to trace the history of risk management decisions and actions is crucial for ensuring transparency and accountability, particularly in cases where the system's performance or behavior changes over time.
In addition to documenting the evolution of risks, providers must ensure that their risk management system is capable of detecting and responding to new risks that may emerge during the system's operation. This requires the implementation of monitoring mechanisms that can identify deviations from expected performance or behavior, as well as changes in the system's usage environment that may introduce new risks. By maintaining a continuous and dynamic risk management process, providers can ensure that their high-risk AI systems remain safe and effective throughout their lifecycle, thereby fulfilling the obligations set out in Article 14 and supporting the broader goals of the AI Act.
Risk Management Lifecycle according to Art. 14
Iterative process that must remain active throughout the system's life.
- 01Risk Identification: Mapping of potential harms to persons, property, or the environment.
- 02Assessment: Analysis of the probability of occurrence and the severity of the impact.
- 03Mitigation: Design and implementation of technical and organizational measures.
- 04Monitoring: Periodic review and upon significant changes to update the risk register.
Initial Assessment vs. Continuous Update
One of the main sources of non-compliance is treating risk management as a single event. The initial assessment is necessary for design and conformity validation, but Article 14 explicitly requires that the system be updated in response to changes in the AI system, its usage environment, or the emergence of new risks. This includes software updates, changes in training data, or modifications in the deployment context.
The difference lies in reactivity. The initial assessment is proactive and design-oriented; the continuous update is reactive and maintenance-oriented. If a provider launches a system and does not establish a mechanism to re-evaluate risks when the model is updated or when a bias is detected in production, they are breaching the obligation to 'maintain' the risk management system. This distinction is crucial for engineering teams, who must integrate risk control points into their deployment pipelines (CI/CD).
The distinction between initial assessment and continuous update is critical for ensuring that the risk management system remains effective throughout the system's lifecycle. While the initial assessment is focused on validating the system's design and conformity with regulatory requirements, the continuous update process is designed to detect and respond to changes that may arise during operation. This includes software updates, changes in training data, or modifications in the deployment context that may introduce new risks or alter the severity of existing ones. By maintaining a clear distinction between these two phases, providers can ensure that their risk management system is both proactive and reactive, capable of addressing both known and emerging risks.
The integration of risk control points into deployment pipelines (CI/CD) is a key aspect of implementing the continuous update process. This involves automating the detection of changes that may impact the system's risk profile and triggering the appropriate risk management actions in response. By embedding risk management into the development and deployment process, providers can ensure that risks are identified and mitigated in a timely manner, thereby reducing the likelihood of non-compliance and enhancing the overall safety and reliability of the system. This approach supports the continuous nature of the risk management obligation and ensures that the system remains compliant with Article 14 throughout its lifecycle.
Differences Between Initial and Continuous Assessment
Comparison of the timing and objectives of each phase.
| Characteristic | Initial Assessment | Continuous Update |
|---|---|---|
| Timing | Pre-launch and design | During operation and after changes |
| Objective | Validate conformity and safe design | Detect emerging risks or context changes |
| Trigger | Development cycle | Updates, incidents, environment changes |
Compliance Checklist and Documentation
To demonstrate compliance with Article 14, providers must align their internal processes with the requirements of Annex IV, which specifies the necessary technical documentation. Having a risk policy is not enough; a living register showing the evolution of each identified risk is required. The documentation must be accessible to market surveillance authorities and must be linked to incident records.
Below is a checklist differentiating between mandatory legal requirements and recommended best practices. Mandatory requirements are those that, if not met, can lead to administrative sanctions. Best practices, while not always explicit in the legal text, are recommended by the Commission and notified bodies to facilitate conformity assessment.
The alignment of internal processes with the requirements of Annex IV is essential for demonstrating compliance with Article 14. This involves ensuring that the risk management documentation is comprehensive, accurate, and accessible to market surveillance authorities. The documentation must include a detailed risk register that shows the evolution of each identified risk, as well as the measures taken to mitigate them. By maintaining a living register that is regularly updated and reviewed, providers can demonstrate that their risk management system is operational and effective, thereby supporting their compliance with the regulation.
In addition to the mandatory legal requirements, providers are encouraged to adopt best practices that facilitate conformity assessment and enhance the effectiveness of their risk management system. These best practices may include the use of harmonized standards, such as ISO/IEC 23894, to guide the implementation of risk management processes, as well as the automation of monitoring activities to detect data drift or performance degradation. By adopting these best practices, providers can not only ensure compliance with Article 14 but also improve the overall quality and reliability of their high-risk AI systems, thereby supporting the broader objectives of the AI Act.
Article 14 Compliance Checklist
Legal requirements vs. best practices.
| Element | Type | Description |
|---|---|---|
| Documented risk register | Mandatory | List of risks, assessments, and mitigation measures. |
| Update process upon changes | Mandatory | Defined mechanism to re-evaluate risks after updates. |
| Linkage with Annex IV | Mandatory | Risk documentation must be part of the technical documentation. |
| Use of harmonized standards (ISO/IEC) | Recommended | Apply ISO/IEC 23894 or other standards to facilitate presumption of conformity. |
| Automation of monitoring | Recommended | MLOps tools to detect data drift or performance degradation. |
Application Dates and Sanctions
The application of Article 14 is subject to the entry-into-force dates of Regulation (EU) 2024/1689. According to Article 113, the regulation enters into force twenty days after its publication in the Official Journal of the European Union. However, the application of provisions relating to high-risk systems (Chapter III) is subject to specific deadlines that depend on the availability of harmonized standards and the supervisory infrastructure. It is crucial to verify the exact application dates for each system category in the consolidated text, as Regulation (EU) 2026/1744 has introduced modifications that may affect these deadlines.
Regarding sanctions, Article 99 establishes a regime of administrative fines. Non-compliance with provider obligations, including the lack of an adequate risk management system, can result in fines of up to €35 million or 7% of the total worldwide annual turnover for the preceding financial year, whichever is higher. These figures underscore the severity of the obligation and the need for rigorous implementation.
The application dates for Article 14 are subject to the entry-into-force dates of Regulation (EU) 2024/1689, which are determined by Article 113. However, the specific deadlines for the application of provisions relating to high-risk systems depend on the availability of harmonized standards and the supervisory infrastructure. This means that providers must carefully monitor the regulatory landscape and verify the exact application dates for each system category in the consolidated text. The introduction of Regulation (EU) 2026/1744 has added complexity to this process, as it may affect the deadlines and requirements for compliance. Therefore, it is crucial for providers to stay informed about the latest developments and to adjust their compliance strategies accordingly.
The regime of administrative fines established by Article 99 underscores the severity of the obligations set out in Article 14. Non-compliance with provider obligations, including the lack of an adequate risk management system, can result in significant financial penalties. These fines serve as a strong incentive for providers to implement rigorous risk management processes and to ensure that their systems are compliant with the regulation. By understanding the potential consequences of non-compliance, providers can prioritize the implementation of effective risk management systems and thereby reduce the risk of facing administrative sanctions.
Limits and Common Confusions
It is important to delimit the scope of Article 14 to avoid overburdening compliance teams. This article does not require the fundamental rights impact assessment, which is a distinct obligation (Article 27) applicable mainly to deployers in certain contexts. It also does not replace the data governance requirements of Article 10, although they feed into each other: poor data governance will generate risks that the risk management system must identify and mitigate.
Furthermore, Article 14 does not obligate real-time human oversight of every system decision, but rather to ensure that the system is designed to be supervised and that the risks associated with the lack of effective oversight are managed. The confusion between 'risk management' and 'human oversight' can lead to incomplete implementations, where investment is made in control interfaces without addressing the root of technical and data risks.
Delimiting the scope of Article 14 is essential for avoiding overburdening compliance teams and ensuring that resources are focused on the most critical aspects of risk management. This article does not require the fundamental rights impact assessment, which is a distinct obligation applicable mainly to deployers in certain contexts. It also does not replace the data governance requirements of Article 10, although both obligations are interconnected. Poor data governance can generate risks that the risk management system must identify and mitigate, highlighting the importance of integrating data governance and risk management processes.
The confusion between 'risk management' and 'human oversight' can lead to incomplete implementations, where investment is made in control interfaces without addressing the root of technical and data risks. To avoid this, providers must ensure that their risk management system is designed to be supervised and that the risks associated with the lack of effective oversight are managed. This requires a holistic approach that integrates technical, organizational, and procedural controls, ensuring that the system remains safe and effective throughout its lifecycle. By clearly distinguishing between these two concepts, providers can ensure that their compliance efforts are focused on the most relevant aspects of the regulation.
Open questions
- The exact application dates for each category of high-risk system may vary depending on the availability of harmonized standards and the modifications of Regulation (EU) 2026/1744, so it is recommended to verify the most recent consolidated text.
- The specific interpretation of what constitutes a 'significant change' requiring the reactivation of the risk management process is not detailed in the legal text and may depend on future Commission guidelines.
Keep exploring
Sources consulted
Corrections and transparency
If you spot incorrect or outdated information, send us a correction with the page and source we should review.
Submit a correction