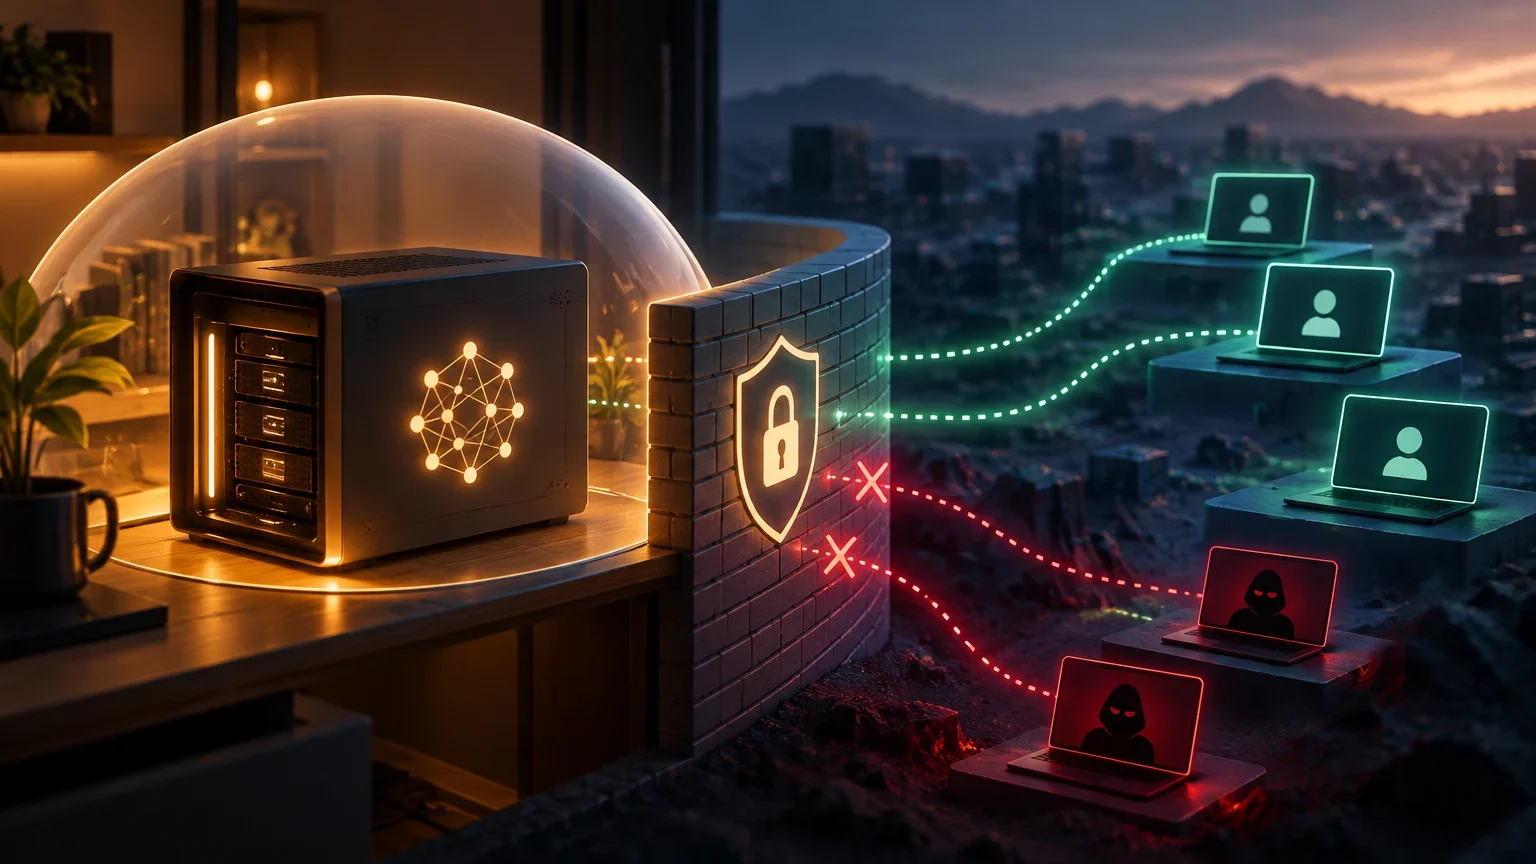
Local Does Not Mean Isolated
A local inference server runs a model on a computer you control, but it may accept requests from other devices if its process listens on an accessible network interface and the machine’s rules allow those connections. The model’s location does not, by itself, determine who can use the API or what they can do with it.
Before sharing the service, define its purpose and access boundary: will it be used only on the host itself, by specific clients on a LAN, or by remote users? Each expansion changes which systems can send data and receive responses. If you cannot identify and verify those boundaries, keep the service restricted to the host or do not enable it.
Map the Request Path
A request typically travels from a client, across the network, to the process exposing the API and the loaded model. It may also pass through a reverse proxy or a web interface. Each component has configuration that can affect access: for example, the client stores credentials, the firewall filters connections, and the runtime serves the endpoint.
Before changing settings, make an inventory: which computer hosts the service, which process runs it, which ports it uses, which clients need access, and whether there are any intermediary components. Also record who can change those controls. Shared inference adds a network path and operational responsibilities that do not arise in the same way when an application runs the model on the device itself.
A minimal request-path map
- 01Client: identify the computer and application that will send requests.
- 02Network: define which interfaces, segments, and routes can reach the host.
- 03Service: check the process, endpoint, ports, and authentication.
- 04Model and data: determine what inputs, outputs, and logs the service handles.
- 05Administration: identify who can change the configuration or credentials.
Choose the Access Scope Before Configuring
If you only need to test the service on the same computer, do not extend access to the LAN for convenience. A loopback address, such as 127.0.0.1 for IPv4 or ::1 for IPv6, limits connections to the host for that protocol and configuration; even so, verify which addresses the process actually uses. A specific network interface or wildcard address may allow other computers to attempt a connection.
To share the service on a LAN, restrict access to the necessary interfaces, networks, and clients, if the runtime and environment allow it. Do not mistake a private network for one where every device is trustworthy. For remote access, review the design again: add suitable controls for the full request path, protect traffic, and avoid publishing a development endpoint directly to the Internet.
Initial decision matrix
| Need | Prudent decision | Condition for proceeding |
|---|---|---|
| Use on the same computer | Keep the service on loopback | Confirm it is not also listening on external interfaces. |
| Use by clients on a LAN | Restrict access to the necessary interfaces, networks, and clients | Test from an authorized client and an unauthorized one. |
| Remote or Internet access | Do not expose a development endpoint directly | Design and verify additional controls across the entire request path. |
| Listening behavior is unknown or boundaries cannot be tested | Do not enable network access | Resolve the configuration and testing gaps before deployment. |
Inspect the Effective Configuration
Do not assume that a runtime listens only on the host or that its initial configuration includes authentication. Defaults depend on the product, version, and launch parameters. Check the current documentation for the runtime you selected, then confirm the result on the host: which address and interfaces are listening, which ports are open, and which process owns them.
Also check how the service handles requests with no credentials, invalid credentials, and disallowed operations. An API that supports a familiar format is not guaranteed to offer the same authentication or authorization features as another product. If the runtime lacks sufficient controls, do not assume that a dummy key or a header sent by the client protects the endpoint.
Apply Controls in Layers
The first layer is limiting where the service listens: use loopback when remote access is unnecessary, or a specific interface when the LAN requires it and the tool supports it. Then configure the operating system or firewall to allow only the intended connections. Rules should match the actual network topology, not the assumption that the entire local network is safe.
Add authentication and authorization when available and needed. Protect credentials, avoid placing them in source code or files that unauthorized users can read, and review the permissions they grant. If you add a reverse proxy, check how it terminates and protects traffic, identifies clients, and whether the origin service is still reachable by another route. Do not use the proxy as a substitute for closing or restricting direct access to the service.
Test from Two Perspectives
A test from the intended client confirms that this route works, but it does not show who else can reach the endpoint. Test from an authorized client and from a device that should not have access. Check the actual outcome, not just whether the application displays an error: a rejected connection, a failed authentication attempt, and a disallowed operation are not necessarily the same thing.
Record the date, runtime version, operating system, source device, network, test method, and result. Repeat the checks after relevant changes to the runtime, firewall, proxy, router, or network topology. A test limited to one LAN does not prove that the endpoint is inaccessible from every other network.
Access test matrix
| Test | Expected result | What to record |
|---|---|---|
| Authorized client with valid credentials | Can access only the intended functions | Source, method, scope, and response. |
| Authorized client without credentials | Request is rejected if authentication is required | Observed response or behavior. |
| Client with invalid credentials | Access is rejected | Observed behavior and available evidence. |
| Client that should not have access | Cannot reach the service or fails its controls | Source network, route, and result. |
| Authorized client attempts a disallowed operation | Operation is denied if function-level authorization is in place | Operation tested and result. |
Logs, Changes, and Maintenance
Decide what information the runtime or proxy should log and who may view those logs. They may contain request or response data, client identifiers, errors, or other sensitive information; review the documentation and effective configuration before retaining or sharing them. Logs can help investigate unexpected access, but their existence alone does not show that access is controlled.
Define who can change network rules, runtime options, and credentials. Keep the runtime and its dependencies updated according to the provider’s instructions, and retest access after updates. If you detect unexpected connections, suspend shared access, review network routes and credentials, and retain the diagnostic information needed under your policies.
Review routine
- 01Document the service’s purpose, permitted clients, and responsible owner.
- 02Review listening interfaces, ports, authentication, authorization, and network rules.
- 03Record what the runtime and proxy retain and who can view it.
- 04Update components through a defined process and review configuration changes.
- 05Repeat access tests and retain the results.
- 06If access is unexpected, restrict or stop the service while you investigate.
When to Keep, Share, or Stop
Keep the service on the host if you only need local use, cannot confidently identify its listening interfaces, or cannot test exposure from another device. Sharing on a LAN may be reasonable when you have defined the clients and networks, applied controls supported by the runtime, and tested both permitted and denied access.
Do not enable access if you cannot restrict who can reach the service, protect credentials, determine what the system logs, or observe and review changes. For remote access, treat the decision as a separate deployment: require a specific review of all components and routes involved, not merely a broader network rule.
Deployment decision
| Review status | Decision |
|---|---|
| Listening behavior and boundaries confirmed; local use is all that is needed | Keep the service on the host. |
| LAN access is needed; scope is restricted and tests are complete | Share with the intended clients and review periodically. |
| Authentication, network restrictions, or testing are insufficient | Do not enable shared access. |
| Remote access is required | Design specific controls and verify them before accepting connections. |
What This Guide Does and Does Not Demonstrate
A connection that succeeds from an allowed client and fails from a test client does not certify that every route is protected. The result depends on the configuration, versions, and topology examined. Nor does it prove that inputs, outputs, or diagnostics stay within a privacy boundary: that requires a separate review of outbound traffic and each component’s behavior.
Access control concerns who can reach the service and what they can do within its limits. Data privacy and outbound traffic are related but distinct questions. Do not infer general security or complete privacy from the fact that the model runs locally or from a single test.
Open questions
- Controls, defaults, and configuration methods vary by runtime, version, and operating system; the available documentation does not support prescribing universal steps.
- No specific network topology, runtime, or tested version is specified for this guide; each deployment must document and repeat its own checks.
- Tests from one authorized and one unauthorized client do not prove that every interface or network route is protected.
- API reachability alone does not reveal whether the runtime, model, or its components make outbound connections or what information their logs retain.
Keep exploring
Sources consulted
Corrections and transparency
If you spot incorrect or outdated information, send us a correction with the page and source we should review.
Submit a correction