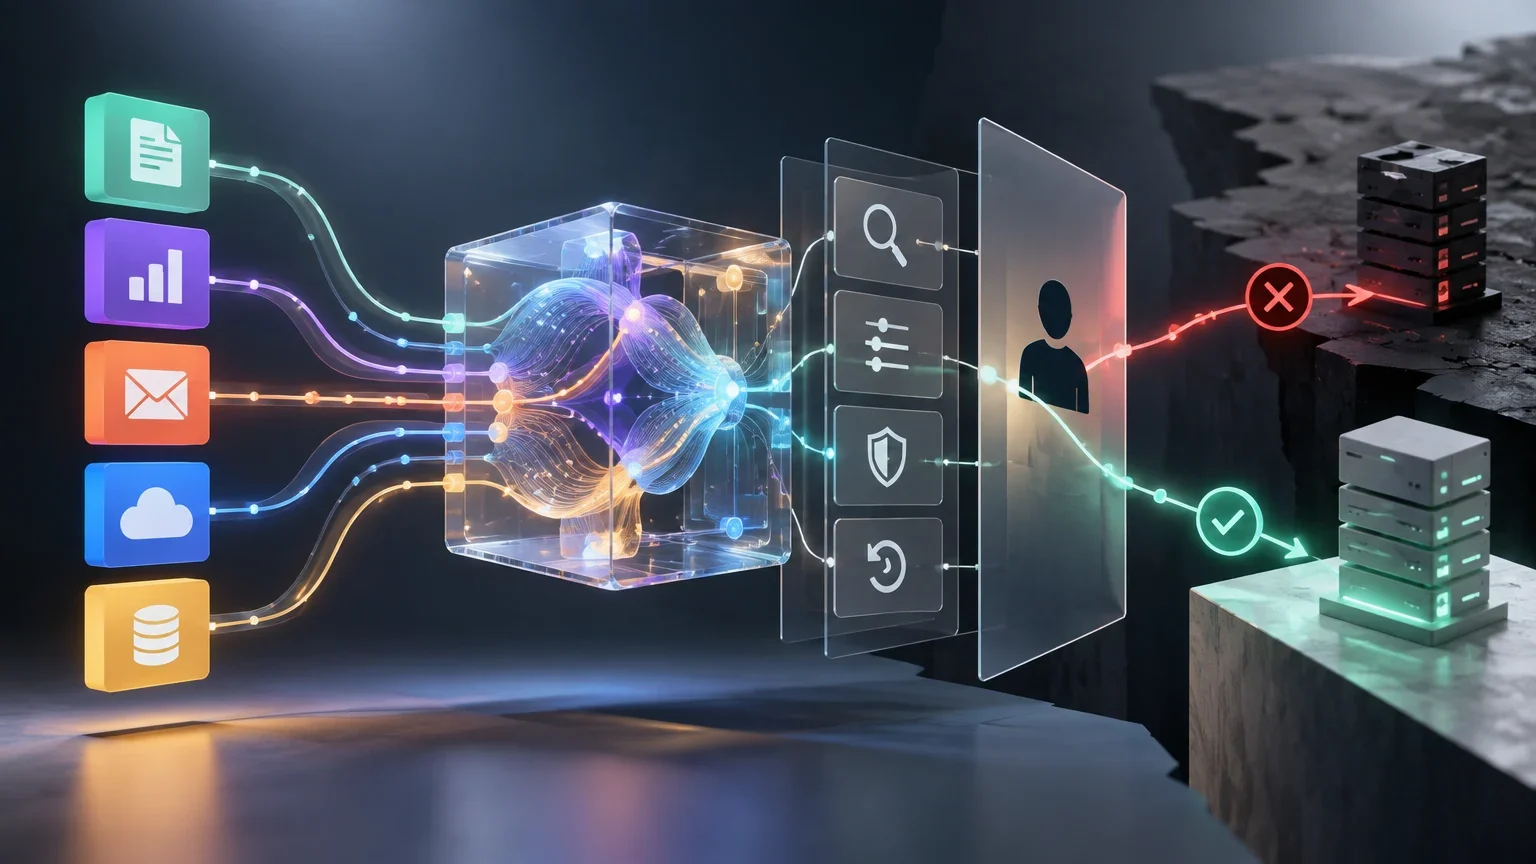
The Real Problem: Connecting Applications Is Not the Same as Automating a Decision
A workflow spanning CRM, email, tickets, documents, spreadsheets, and internal systems is often presented as a simple chain: data arrives, a model interprets it, and an application receives an action. That description leaves out the parts that determine operational risk. You need to know which event started the run, which data was given to the model, which rule constrained its response, which validation was applied, who authorized the action, and what the destination system confirmed.
AI can add value to tasks with unstructured or variable inputs, such as summarizing an email, extracting fields from an invoice, or proposing a category for a ticket. On its own, however, it does not turn the result into a reliable instruction to modify a record, send a communication, or close a case. A model output should be treated as a proposal that needs an expected format, value limits, business rules, and, depending on the impact, human review.
Tool selection should begin with the process rather than the integration catalog. Two tools may connect the same applications yet differ significantly in their ability to test a change, retain history, separate configurations, compare versions, or stop a risky action. These capabilities matter when a classification is wrong, a document is incomplete, an integration gives an ambiguous response, or a run is repeated after a network failure.
It is also useful to separate two questions that are often mixed together. The first is whether the workflow can produce a useful decision. The second is whether the organization can inspect that decision, correct it, and recover from its effects. This guide focuses on the second question. It does not assess the inherent quality of models or promise autonomy; it provides a way to decide which operating architecture and minimum controls each use case requires.
When exploring tools in the site’s discover, compare, and learn sections, use the same business case and the same test data. This prevents you from attributing differences to the platform when they actually result from a different trigger, a different model instruction, or a different credential configuration.
The Four Architectures: Choose the Degree of Automation by the Risk of the Action
The right architecture depends on the nature of the input and on the consequence of being wrong. A reversible internal recommendation does not need the same controls as a financial update, a message to a customer, or the closure of an incident. Volume matters, but it does not replace impact analysis: a small error repeated thousands of times can cost more than an isolated high-impact error.
The first architecture is deterministic rules with AI assistance. The model summarizes, translates, extracts terms, or drafts content, while rules determine routing and action. It is suitable when the decision can be expressed through stable, verifiable criteria. For example, a rule assigns tickets by product and service level, while AI only produces a summary for the receiving agent.
The second architecture is extraction and routing. Here, AI transforms a variable input into structured fields, and the workflow sends the case to a queue, system, or owner. It works best when the output set is bounded: document type, language, permitted priority, or request category. It should include schema validation, allowed values, and an explicit path for incomplete, contradictory, or out-of-classification data.
The third architecture is integrated human review. The workflow assembles context, prepares a proposal, and pauses until a person approves, rejects, or edits it. Power Automate documentation describes flows that can wait for an approval decision, while Zapier documentation describes data-collection or approval requests before later workflow actions continue. These capabilities are useful when the criterion requires judgment, the data is sensitive, or the error is not easily reversible. They do not remove human accountability; they make the point at which the decision is made visible.
The fourth architecture is bounded autonomous execution. The workflow can complete an action without case-by-case approval, but only within a defined scope: specific fields, authorized applications, limited amounts or statuses, execution windows, and blocking rules. This is an option for frequent, low-impact, reversible tasks after evidence has shown that expected inputs and failures are covered. It should not be the starting point for irreversible actions or broad-scope changes.
The word “autonomous” should not mean the absence of controls. In a bounded architecture, autonomy is constrained through permissions, validations, thresholds, logs, and stop mechanisms. If the tool does not show precisely which version performed an action, with which input, and with which result, the organization will struggle to extend that pattern responsibly.
Operating architectures and threshold for use
| Architecture | Primary use | External action | Minimum control |
|---|---|---|---|
| AI assistance with rules | Summaries, drafting, or contextual support | Decided by fixed rules | Input validation and output logging |
| Extraction and routing | Turn documents or messages into fields | Send to a queue or create a draft | Schema, allowed values, and an exception path |
| Integrated human review | Ambiguous or sensitive cases | Only after approval, rejection, or editing | Sufficient context, an accountable owner, and decision evidence |
| Bounded autonomy | Repeatable and reversible tasks | Within predefined limits | Scope limits, confirmation, and reversal or reconciliation |
Workflow Map: From a Trigger to Verifiable Recovery
Before evaluating a platform, map the entire workflow. The trigger identifies what starts it: a received email, an uploaded document, a status change, or a new row. Next comes context: customer data, ticket history, document fields, applicable rules, and any information provided to the model. Context must be sufficient to make a decision, but no broader than necessary, especially when it contains personal or confidential data.
The decision transforms that context into an operational output, such as a category, a set of fields, or a proposed reply. Validation checks that the output exists, follows the format, belongs to the permitted set, and is consistent with rules independent of the model. The action may create, modify, send, escalate, or block something in another application. Logging preserves the evidence needed to understand the run. Recovery determines what to do if the action failed, ended in an unknown state, or was only partially completed.
This map reveals a fundamental distinction between failure and ambiguity. A clear failure is, for example, an explicit rejection response from the destination system. An ambiguous outcome occurs when the wait time expires after sending the request: the destination may have performed the update even though the workflow received no confirmation. Automatically retrying without an idempotency key, a verification query, or a reconciliation rule can duplicate a message, order, or record.
Testing tools should be assessed against these situations. Microsoft guidance on testing cloud flows refers to test data and run history, and warns that resubmitting a run can create duplicates depending on the actions involved. Therefore, “run it again” is not the same as “recover safely.” Ask which steps will be repeated, which can be queried before repetition, and how attempts are linked to the original operation.
Traceability does not mean retaining everything forever. Microsoft documentation indicates that inputs and outputs may be visible in run history and that options exist to secure them. Hiding sensitive data reduces exposure but can limit later investigation. The decision should document which fields are masked, which non-sensitive identifiers remain available, who can inspect the logs, and for how long.
Minimum design for a recoverable run
- 01Define the triggering event and assign a correlation identifier to the run.
- 02Retrieve only the needed context and log stable references to the source data.
- 03Obtain a structured output from the AI component and validate fields, types, and allowed values.
- 04Apply deterministic blocking rules, scope limits, and, where appropriate, human approval.
- 05Request the external action with a key that helps detect duplicates when the destination system supports one.
- 06Confirm the status by querying the destination system or recording a verifiable response.
- 07For an ambiguous result, send the case to reconciliation before repeating an action with external effects.
- 08Record the workflow version, validation results, and recovery decision.
Selection Criteria: Testing, Evidence, Limits, and Data
Connectors are a compatibility requirement, not a guarantee of control. Check that they cover the specific actions the process needs: reading a change, querying a status, creating a draft, updating a field, attaching evidence, or cancelling an operation. A connector that can only create objects but cannot query their result makes reconciliation harder. Likewise, an available integration does not confirm that it exposes the fields needed to validate the action.
Require practical separation between development, test, and production. Power Automate environment variables are documented for changing configuration values across environments when solutions are exported and imported. This matters because it can preserve workflow logic while replacing destinations, identifiers, or parameters. Even so, verify in every tool how changes are promoted, which elements fall outside version control, and whether a test credential can accidentally act on real data.
Versioning should answer operational questions: which version ran, what changed from the prior version, and how to return to a known version. Zapier documents drafts and versions, including comparison and reversion to a previous version in certain contexts. That supports treating versioning as an evaluable product capability, but it does not by itself prove a complete deployment strategy. You need to test whether model instructions, validations, schemas, parameters, and connection references are also versioned.
For each run, the minimum desirable evidence includes the trigger, references to context, validated output, applied rules, the approval if present, the requested action, and the observed result at the destination. Zapier documents a run history that can be filtered, among other criteria, by version. Confirm which content is actually shown, how long it is retained, and what happens to hidden or protected information. Do not mistake the existence of a history dashboard for an adequate retention, access, and export policy.
Execution limits should be close to the risky action. A general approval rule for the entire workflow can introduce unnecessary delays, whereas a localized rule can block only the external send or the modification of a sensitive field. Power Automate data loss prevention policies can control connectors and their combination within environments. This illustrates a useful control to assess: preventing certain data from moving between incompatible services before the workflow runs.
Data review should cover residence, retention, access, and trace content. The available sources do not establish a general answer for every platform about where data is hosted, how long it is kept, or what data a connected model processes. Request these terms from the provider and compare them with applicable internal and regulatory policies. If the response does not distinguish run data, files, credentials, logs, and data sent to AI services, that is a material uncertainty.
Procurement questions and evidence worth requesting
| Capability | Verification question | Practical evidence |
|---|---|---|
| Environments | Is testing isolated from real actions? | Promote the same workflow from test to production with different destinations and without changing its logic. |
| Versioning | Can a prior configuration be identified and restored? | Compare two versions and return to a known one; check which elements are included. |
| History | Can the full decision chain be seen? | Inspect a run with its input, validation, action, and destination result. |
| Approval | Can only the sensitive action be paused? | Approve, reject, and edit a proposal without blocking the rest of the processing. |
| Recovery | How does it handle an ambiguous timeout? | Simulate a lost response and verify that the action is not duplicated. |
| Data | What is retained and who can see it? | Review options for masking, retention, permissions, and log export. |
What to Require by Process and How to Run a Reproducible Procurement Test
Ticket triage usually fits extraction and routing. AI can propose a category, urgency, and summary; rules should constrain categories, detect missing fields, and send low-certainty cases to a human queue. Before allowing automated closure, check whether the workflow can distinguish a suggestion from a confirmed resolution and whether it retains the reason for each routing decision.
CRM enrichment requires particular attention to provenance and overwriting. A tool may add derived data from an authorized source, but it should not replace a person-maintained field without an explicit rule. Start by creating proposed-value fields, an update date, and a source; promote values to canonical fields only after validation. If updates are automated, limit the objects, fields, and statuses that the workflow can modify.
Document extraction benefits from clear schemas and an exception path. Define mandatory fields, acceptable formats, and documents that must be rejected because of poor readability or inconsistency. For documents with contractual, financial, or regulatory consequences, extraction should not replace appropriate review. Volume alone is not a sufficient reason to omit controls when extracted data triggers a payment, commitment, or change in obligation.
For email replies, the risk depends on the recipient and the effect of the message. An internal reply or a draft can be automated more readily than a final external communication. Require allowlists of recipients, approved templates where appropriate, blocks on unauthorized attachments, and confirmation that the message was sent. A reviewable draft is usually a more prudent architecture for initial deployments.
For internal-system updates, the central requirement is the ability to query the resulting state and restore or compensate for the change. When no technical reversal exists, reduce autonomy: use approval, create a change record, and design a correction procedure. An irreversible action does not become safe merely because it runs quickly.
The procurement test should be reproducible and applied to finalists with the same dataset. Prepare at least four cases: a normal one, an ambiguous input, an integration failure, and an action that policy must block. Measure not only whether the workflow completes, but also what evidence it leaves, which person or rule made the decision, whether it can be repeated without duplicating effects, and how long it takes to detect an abnormal state.
In the normal case, review the business result and its confirmation at the destination. For an ambiguous input, verify that the workflow does not invent a value or force a category: it should request information, divert the case to review, or stop. For the integration failure, simulate both a rejection response and a lost response; they are different scenarios. For the blocked action, attempt a modification outside the permitted scope and confirm that the barrier applies before the external action, leaves a record, and cannot be bypassed by changing the input text.
The final decision can be summarized in a simple matrix. The lower the reversibility and the higher the impact, the closer human control should be and the stricter the evidence requirements must become. With a higher volume of low-impact actions, bounded autonomy may be justified, provided the system demonstrates validation, limits, and reconciliation. If it cannot demonstrate them in a test, keep the process in a less autonomous architecture.
Procurement test in four scenarios
- 01Configure a test workflow with synthetic or authorized data and a non-production destination.
- 02Run a normal case and check the final result in the destination application.
- 03Run an ambiguous input and verify that the exception path or human review is triggered.
- 04Simulate an explicit integration rejection and review the log and notification.
- 05Simulate a timeout after requesting an action and check the reconciliation procedure before any retry.
- 06Attempt an action prohibited by scope, field, recipient, or business rule.
- 07Compare the runs: version used, visible data, decisions, timings, actions performed, and ability to correct.
- 08Document the results and retain as a requirement every control that prevented an erroneous action.
Final selection matrix
| Impact and reversibility | Volume | Recommended starting architecture | Minimum capabilities |
|---|---|---|---|
| Low impact and easily reversible | Low or medium | AI assistance with rules | Fixed rules, basic validation, history, and destination confirmation |
| Moderate impact and structured output | Medium or high | Extraction and routing | Schema, allowed values, exception queue, testing, and versioning |
| High impact or ambiguous criterion | Any volume | Integrated human review | Approval or editing, visible context, decision evidence, and auditability |
| Low impact but very high volume | High | Bounded autonomy after testing | Action limits, duplicate detection, reconciliation, stop mechanism, and periodic review |
| Irreversible or consequential | Any volume | Human review or process redesign | Independent confirmation, segregation of duties, and a correction procedure |
Open questions
- The supplied sources describe specific Microsoft Power Automate and Zapier features; they do not support generalizing their capabilities to every automation tool.
- Feature availability may depend on the purchased plan, region, connector type, environment configuration, and later provider changes.
- The supplied sources do not establish a common policy for data residence, retention, access, or use across all platforms and connected AI services.
- Classification, extraction, or generation quality depends on the model, instructions, data, and process validations; it cannot be inferred from the presence of an integration.
- Actual reversal also depends on the destination system’s capabilities: restoring a workflow version does not necessarily undo actions that have already run.
Keep exploring
Sources consulted
Corrections and transparency
If you spot incorrect or outdated information, send us a correction with the page and source we should review.
Submit a correction